📊 Full opportunity report: Device Security Checker For Remote Teams' Mixed Hardware on IdeaNavigator AI — validation score, market gap, and execution plan.
Get ready for Prime Big Deal Days — try Prime free
Exclusive member deals on October 6–7, plus fast free delivery. Cancel anytime.
Start your free trialAs an affiliate, we earn on qualifying purchases.
TL;DR
A new device security checker for remote teams with mixed hardware is in development, targeting SMBs facing compliance requirements. It offers a lightweight, voluntary agent to verify device security posture, with potential to streamline audits and improve security.
A new security verification tool is being developed specifically for remote teams using diverse, employee-owned hardware. The lightweight agent, which employees install voluntarily, assesses device encryption, OS updates, screen lock status, and password manager presence. This approach aims to fill a verification gap created by the limitations of traditional mobile device management (MDM) solutions on unmanaged devices, providing companies with a scalable way to demonstrate compliance during audits and security reviews.
The proposed device security checker targets small and medium-sized businesses (SMBs) with remote teams, where employees use a mix of personal MacBooks, aging Windows laptops, and unmanaged smartphones. Currently, many companies lack visibility into whether these devices meet security standards such as disk encryption, recent OS updates, or enforced screen locks. This gap poses a risk during compliance audits, especially with increasing demands from frameworks like SOC 2.
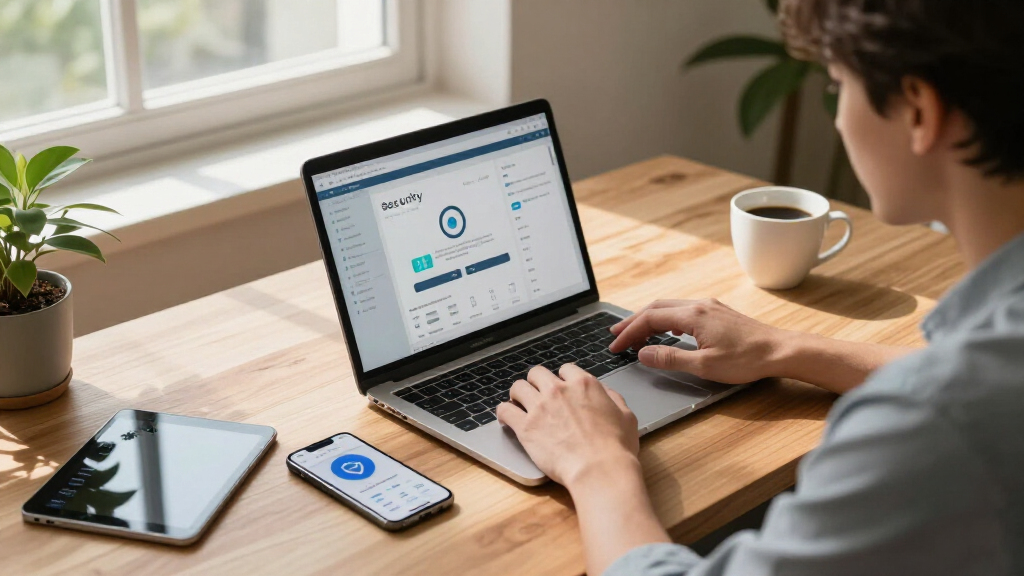
The tool under development is a lightweight agent that employees can voluntarily install, which then checks for key security indicators. It reports a pass or fail status to a centralized dashboard, allowing security teams to identify vulnerabilities quickly. Unlike traditional MDM, this solution does not require remote control or invasive management, making it more acceptable to employees and easier to deploy at scale. The system also provides self-remediation instructions, guiding users to fix issues directly on their devices.
Pricing for the service is expected to be per-device monthly, with additional features such as compliance report exports available on paid tiers. Early validation efforts involve deploying the tool at ten remote startups that are preparing for SOC 2 audits, measuring device enrollment rates, and assessing whether auditors accept the generated posture reports as sufficient evidence of security compliance.
Implications for SMBs and Remote Security Compliance
This development could significantly impact how remote companies demonstrate compliance and manage security risks without resorting to invasive management tools. As frameworks like SOC 2 demand continuous verification of device security, the ability to quickly verify device posture on personal hardware becomes critical. The lightweight agent approach offers a scalable, employee-friendly alternative to traditional MDM, potentially reducing costs and friction while improving security assurance.
For security teams, this tool provides a clearer picture of device vulnerabilities, enabling targeted remediation and proactive risk management. It also aligns with increasing regulatory scrutiny and customer expectations for data protection, making it a relevant solution for SMBs seeking to maintain trust and compliance in a remote-first environment.
device encryption checker software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for Verification of Employee-Owned Devices
Remote work has surged over recent years, leading to a proliferation of employee-owned devices accessing corporate data. Many companies rely on MDM solutions to enforce security policies, but these tools often prove too invasive or impractical for unmanaged hardware, especially personal smartphones and laptops. As a result, organizations face a verification gap during audits and security reviews, which can delay compliance and increase risk.
Regulatory frameworks like SOC 2 now require ongoing evidence that devices meet security standards, including encryption, updates, and access controls. However, traditional solutions are often too heavy-handed or incompatible with employee-owned hardware, creating a need for lightweight, voluntary verification tools. Early-stage startups and SMBs are particularly vulnerable to these gaps, as they lack the resources for extensive device management but still face compliance pressures.
This context has driven interest in minimal, user-friendly security checkers that can integrate seamlessly into remote workflows, providing assurance without disrupting employee productivity or privacy.
Uncertainties About Adoption and Audit Acceptance
It is not yet clear how quickly remote companies will adopt this new verification tool or whether auditors will accept its reports as sufficient evidence of security posture. The initial deployment phase involves testing at ten startups, but broader industry validation remains to be seen. Additionally, questions about the tool’s ability to accurately detect vulnerabilities across diverse hardware and OS versions are still under assessment.
Further, the long-term compliance benefits depend on widespread acceptance by auditors and regulatory bodies, which may require additional validation and standardization. The effectiveness of self-remediation instructions and user compliance also remains to be proven in real-world scenarios.
Next Steps for Deployment and Industry Validation
The startup plans to pilot the device security checker at ten remote SMBs over the next three months, focusing on device enrollment rates and feedback from security teams. Success metrics include high adoption rates, accurate reporting, and positive auditor feedback. If initial results are favorable, broader rollout and integrations with existing security workflows are expected.
Further development will likely include refining detection capabilities, expanding device support, and exploring integrations with other security tools. Industry validation through pilot programs and potential partnerships with compliance providers could accelerate adoption, while ongoing feedback will shape future enhancements.
Key Questions
How does the security checker work without remote control?
The agent runs locally on the device and performs security checks such as encryption status, OS updates, and screen lock presence. It then reports the results to a central dashboard without needing remote access or control over the device.
Is the tool suitable for all types of devices?
The initial focus is on common endpoints like MacBooks, Windows laptops, and smartphones. Support for other device types may be added as the product develops, but compatibility details are still being finalized.
Will employees need to manually run the checks?
The agent is designed to be installed voluntarily and run automatically or on demand. The process is intended to be simple and minimally disruptive to encourage adoption.
How will this tool impact existing security workflows?
It aims to complement existing security measures by providing quick, scalable verification reports that can be integrated into compliance and audit processes, reducing manual checks and increasing visibility.
When will this tool be generally available?
The initial deployment is planned within the next three months, with broader availability depending on pilot results and industry validation.
Source: IdeaNavigator AI
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.